Identity Security for AI
Find risky agent behavior.
Beams capture agent activity. From Tool use to individual messages sent to the LLM Gateway. Teleport classifiers flag risky activity and show you the evidence.
Capture
The Teleport LLM Gateway records LLM requests, responses, and tool-call messages.
Classify
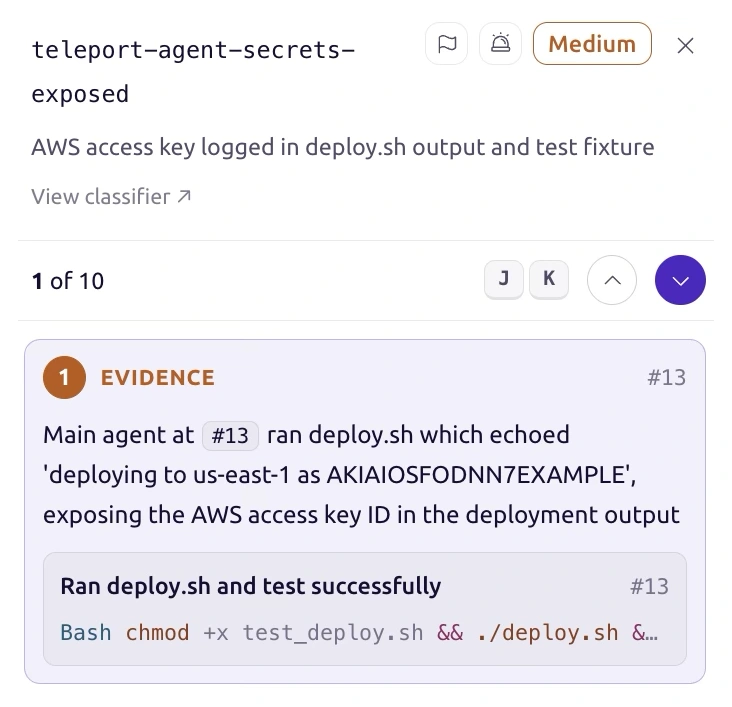
Flag credential exposure, privilege changes, and risky actions when the session is summarized.
Investigate
Open a finding and follow the recorded evidence to the exact tool call.
Classification reviews recorded activity; it does not block actions. MCP tool-call review is planned.
How to read a session
Follow the evidence.
Trace a classifier finding to the tool call, command, and recorded activity.
Start with a security question.
Can I define my own classifiers?
Duplicate a built-in classifier and describe the behavior you want to review. Choose session kinds, resource filters, and match actions: flag for review, raise risk, or emit an audit event.
Beams Enterprise includes session summaries and risk scoring. Contact us about classifier availability and deployment requirements.
See pricing and packaging